CRA compliance,built into yourengineering.
From threat model to technical file. We guide the analysis and build a chain that collects the evidence with every release. Your own team keeps that chain running afterwards.
- Threat
- Requirement
- Control
- Test
- Evidence
- Release
Since September 11, 2026, you must report actively exploited vulnerabilities and severe incidents, also for products already on the market. The full CRA applies from December 11, 2027.
What you must be able to demonstrate from 2027.
A secure product
Secure by default, a limited attack surface and security updates.
Handling vulnerabilities
An SBOM, fast and free patches, a vulnerability disclosure policy and a contact address for reports.
A risk assessment
Mandatory, documented and reviewed again with every release.
A file that stays current
Kept for at least ten years. Updates for at least five years, unless the product is expected to be in use for a shorter time.
Fines for non-compliance of up to €15 million or 2.5% of worldwide annual turnover. Sources: Regulation (EU) 2024/2847 and the European Commission. This page is a summary, not legal advice.
Your team builds the evidence while it develops.
Threat model analysis
Together with your engineers, we map the threats, risks and controls for each interface. Your team learns the method and applies it on its own afterwards.
Full traceability
Every threat, requirement, test and report gets one ID, linked to the CRA requirements. You see right away where evidence is missing or a test fails.
In your existing tools
Repositories, CI/CD, requirements management and release process. We replace nothing; we connect what is already there.
One ID, from threat to file.
- T-014Threat
- SEC-014Requirement
- C-07Control
- TC-104Test
- reportEvidence
- v1.2.0Release
When an audit comes, your file is already up to date.
The chain in one application, installed on your premises.
The application takes every product through eight steps, from scope to report. It runs entirely on its own in your environment, without cloud or subscription.
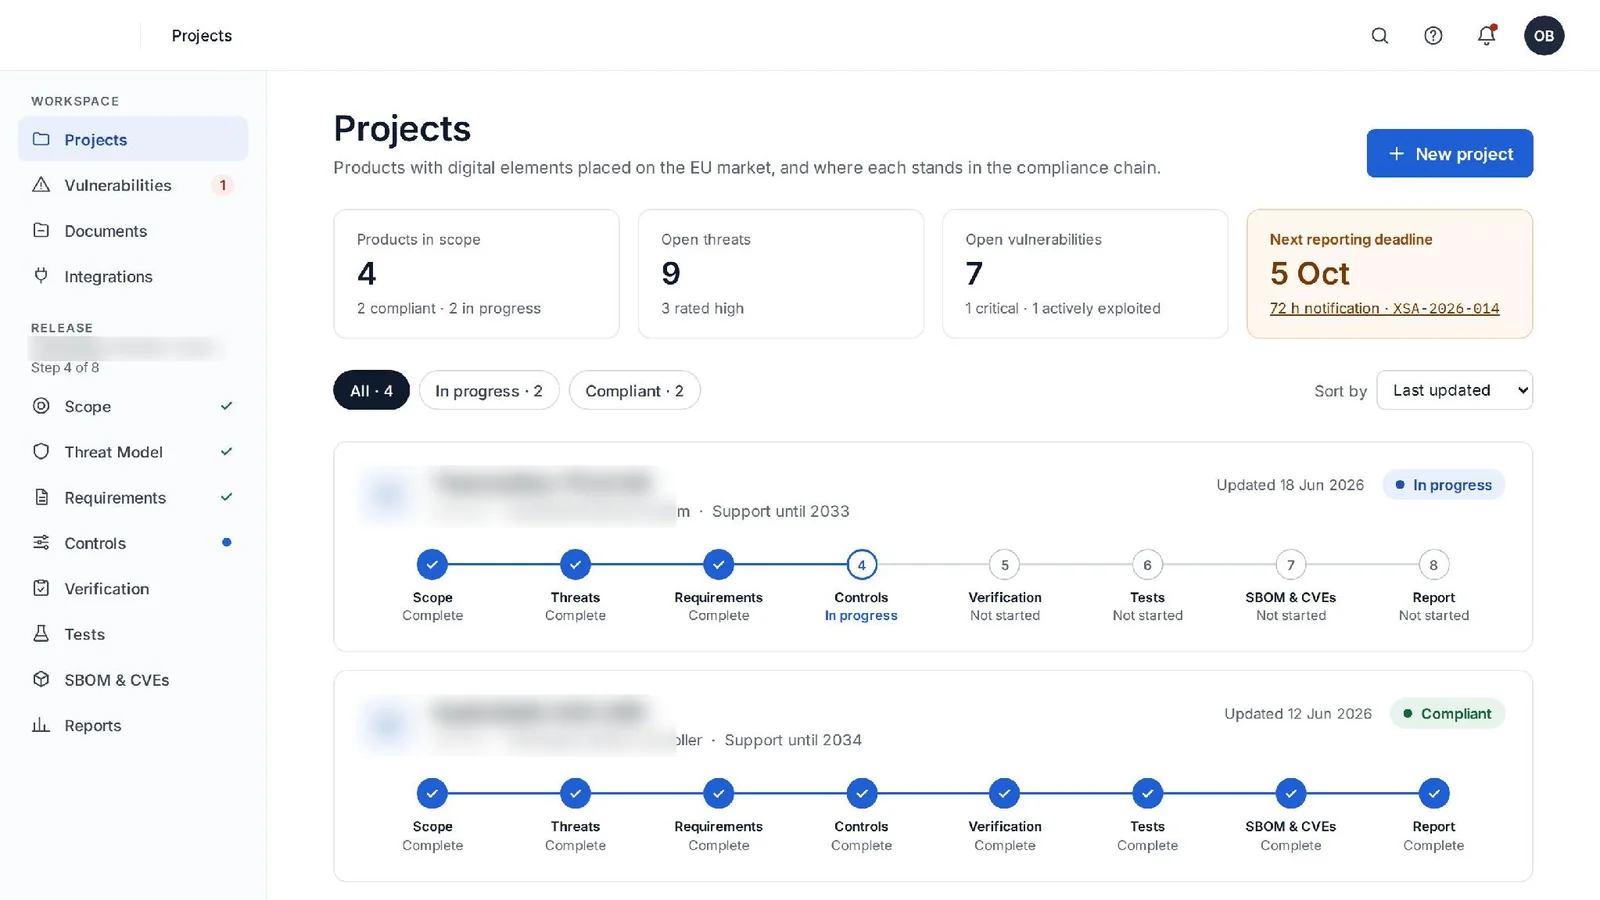
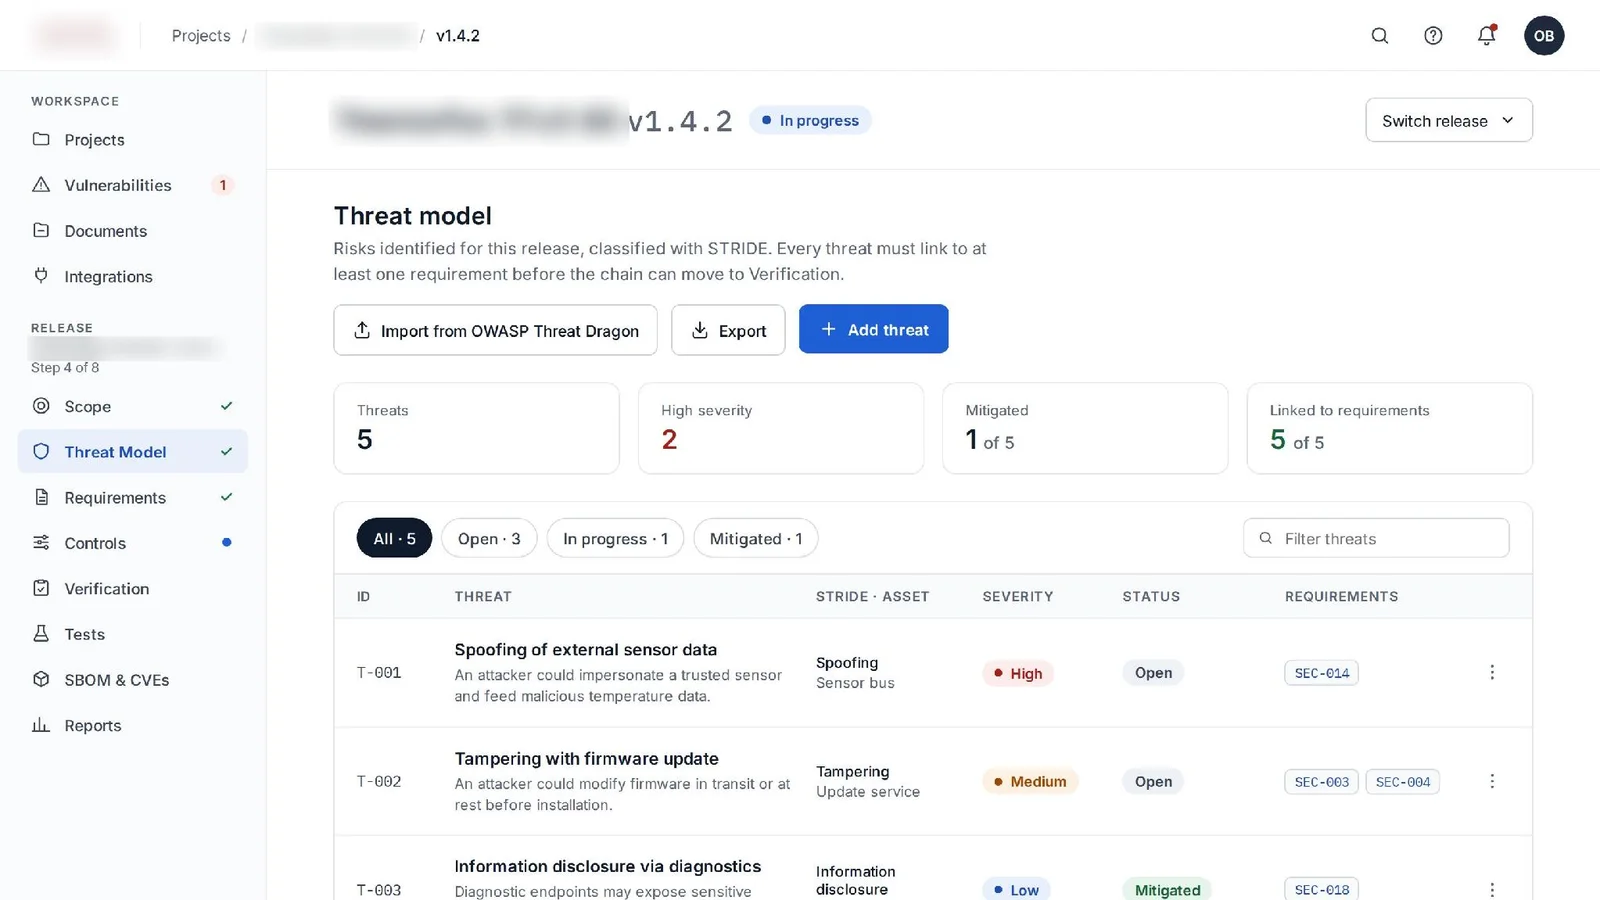
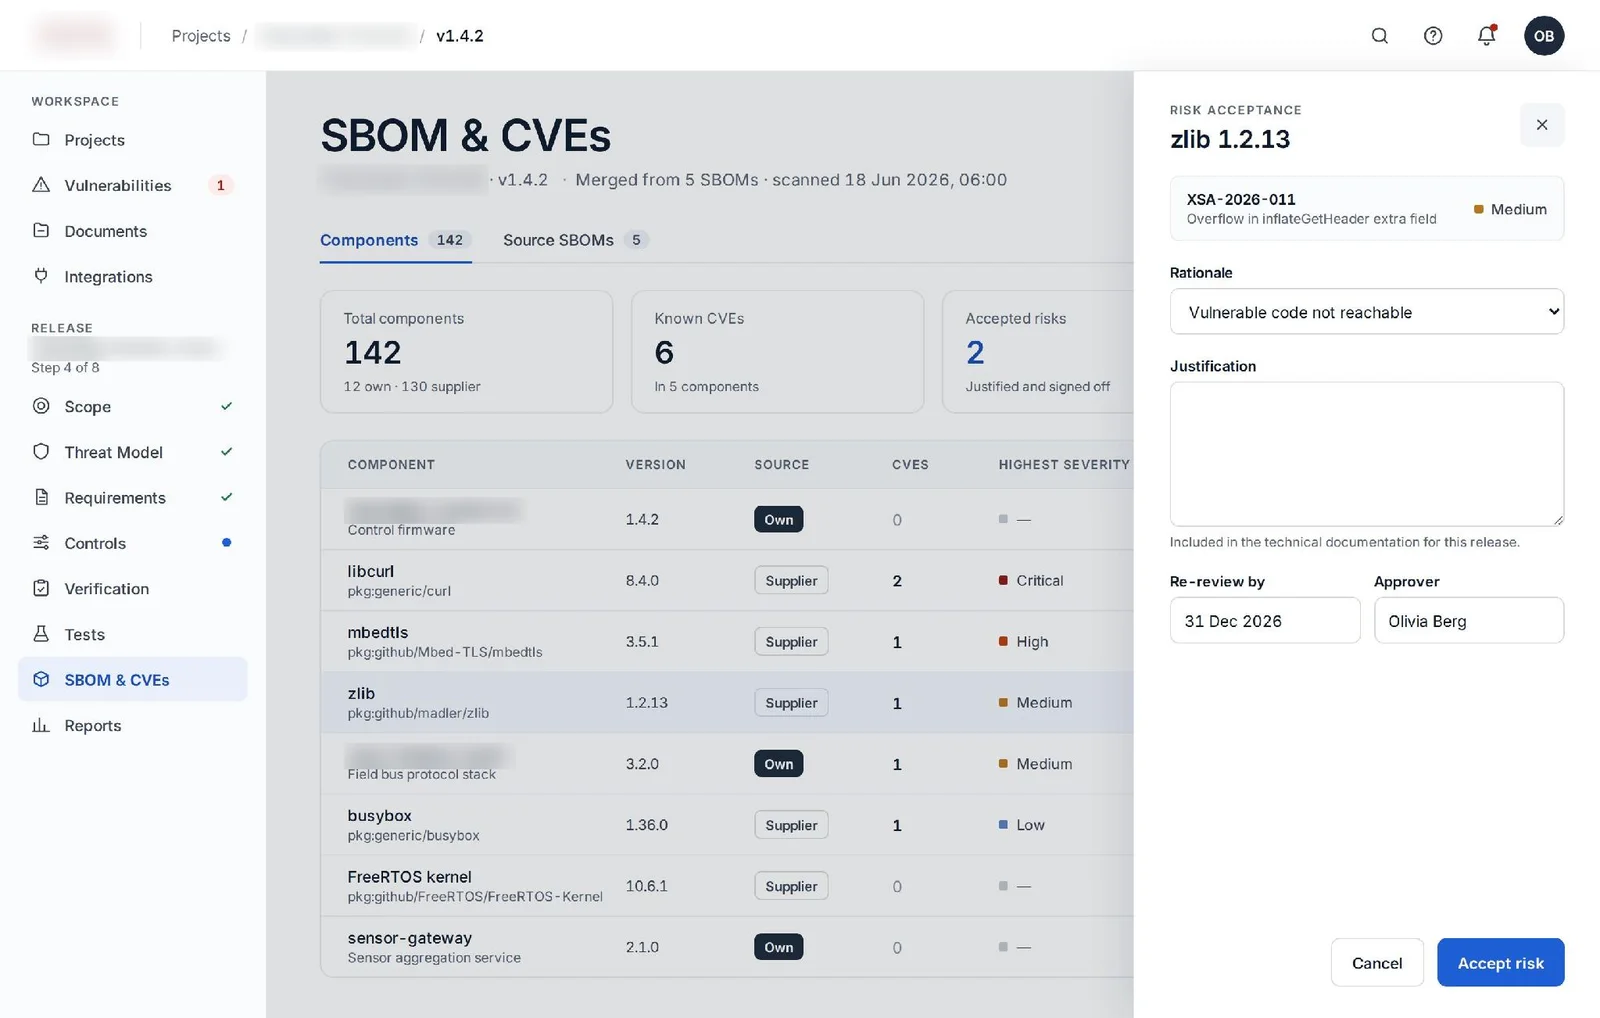
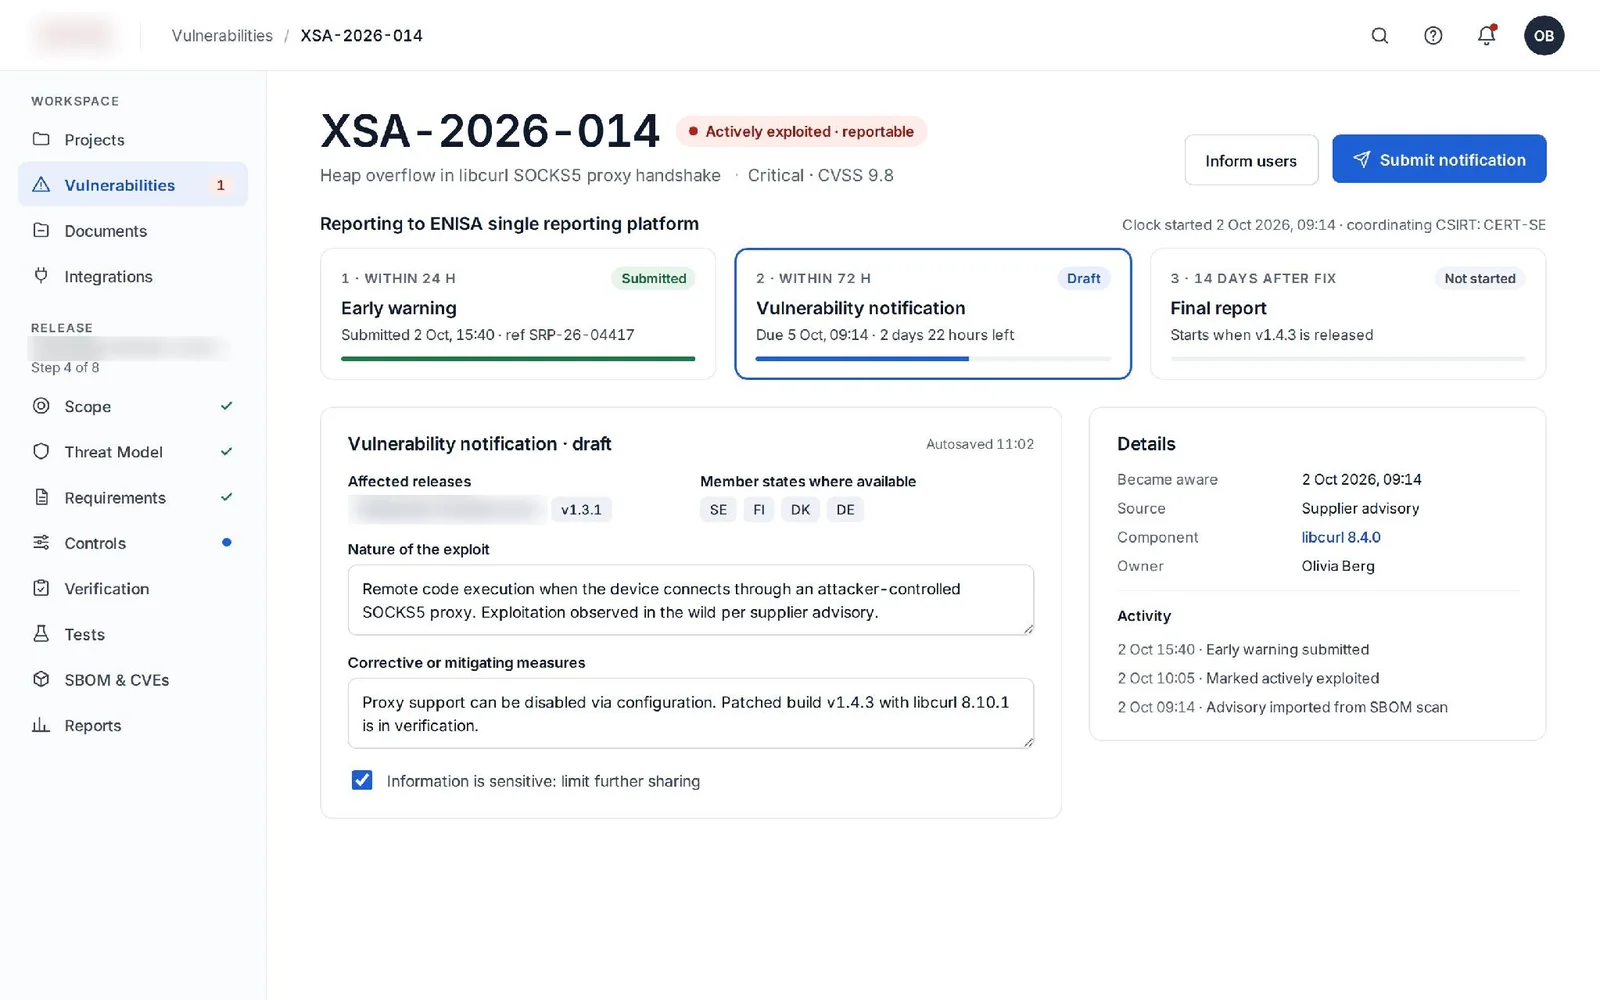
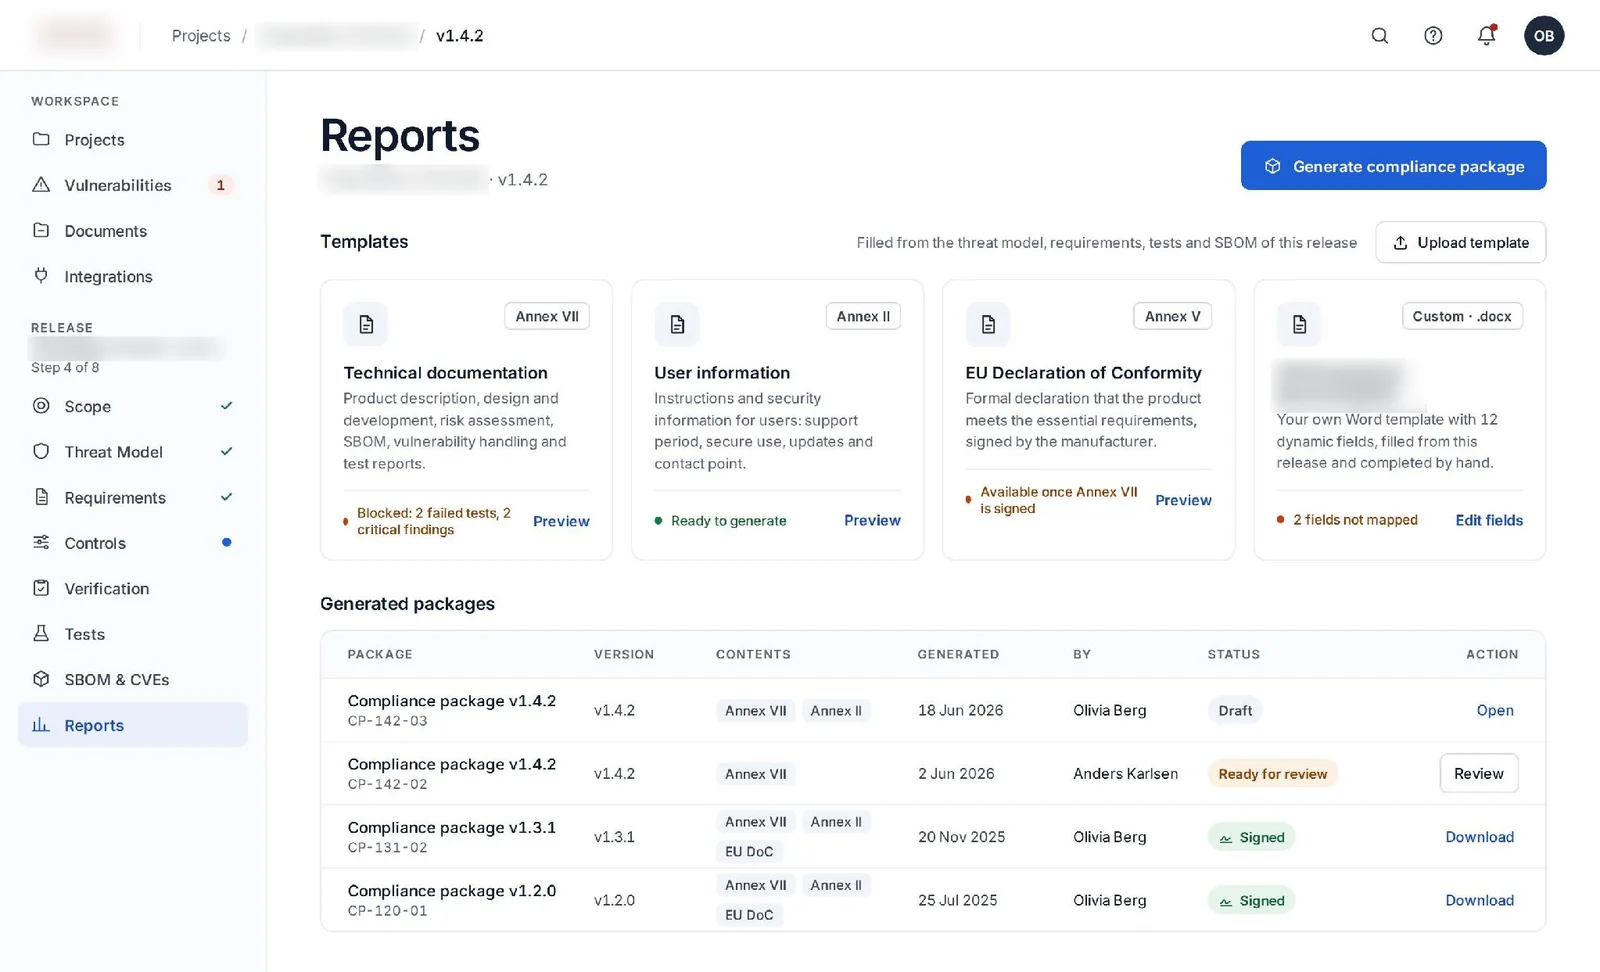
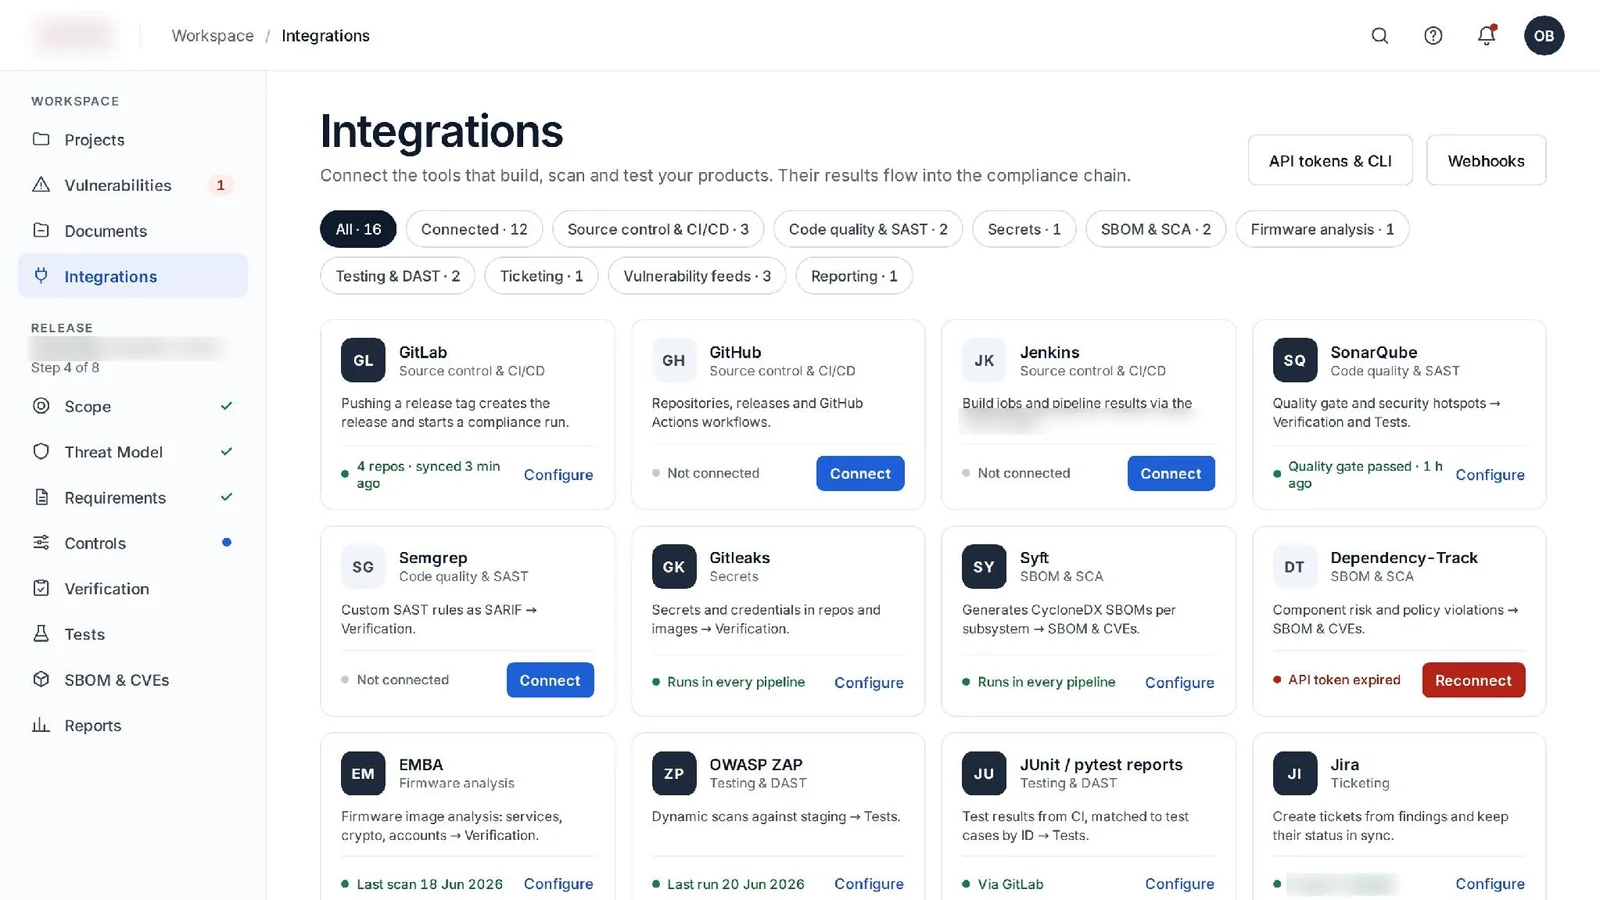
A complete file after every release, in your own environment.
- Annex VIITechnical file, continuously updated
- Annex IIUser information
- Annex VDraft EU declaration of conformity
- LifecycleSBOM, vulnerability status and test evidence
- Article 14Reporting process and playbook for CSIRT and ENISA
No SaaS, no lock‑in.
The chain runs in your own engineering environment. You remain the manufacturer: risk acceptance, notifications, the EU declaration and CE marking stay with you. We deliver the engineering and the evidence.
Let's look together at how we can make your product comply with the CRA.
In a first conversation, we look together at whether the CRA applies to your product, which class and route are likely to apply and what the best first step is.
8500 Kortrijk